> For the complete documentation index, see [llms.txt](https://docs.lightbeam.ai/lxqobxw6ak7CTnsQjikH/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.lightbeam.ai/lxqobxw6ak7CTnsQjikH/core-features/spectra-ai/playbooks/policy-and-alerts/how-to-create-a-rule-set.md).

# How to create a rule set

***

To create a new rule set, follow these steps:

### **1. Create New Rule Set**&#x20;

Click on **Create New Rule Set** at the top right corner.

<figure><img src="https://682442409-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F0FnJiPbEPpkm5U4tiZUM%2Fuploads%2FF2QvXUG30TZ9xliN2KKU%2Fplaybooks%207.png?alt=media&amp;token=d24e84f2-3276-424f-a2c3-c4125f2400eb" alt="" width="193"><figcaption><p>Figure 7: Create New Rule Set</p></figcaption></figure>

### **2. Select Policy Type**

**Rule Set Name and Policy Type:** **-**

* Select a policy type (**`Detection`**, **`External Users`**, **`Internal Users`**, **`Labeling`** or **`Retention`**).

<figure><img src="https://682442409-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F0FnJiPbEPpkm5U4tiZUM%2Fuploads%2Fhsx03np48VmgIz0AHfbN%2Fimage.png?alt=media&amp;token=3060691a-02ab-4c41-90bb-7ab9b8787d97" alt=""><figcaption><p>Figure 8: Selection of Policy Type</p></figcaption></figure>

* Enter a name for the new rule set.<br>
* Enter a description.

<figure><img src="https://682442409-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F0FnJiPbEPpkm5U4tiZUM%2Fuploads%2FTifbNhUvlzkuyK22w3xS%2Fimage.png?alt=media&amp;token=69c69a22-ef5c-490a-b3bf-eeb74f7dda6a" alt=""><figcaption><p>Figure 8.1:  Rule Set Name &#x26; Description<br></p></figcaption></figure>

***

### **3. Rule Set Criteria**

The **Rule Set Criteria** screen allows you to define the conditions under which alerts are triggered. This is the first step in creating a rule set and supports combining multiple conditions with logical operators like OR or AND. You can configure conditions based on document classification, sensitive attributes, sensitivity levels, or labels.

The following steps explain how to configure Rule Set Criteria, referencing the diagram for better visualization.

<figure><img src="https://682442409-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F0FnJiPbEPpkm5U4tiZUM%2Fuploads%2FHEtz6yqZOUCNTbDoqoHF%2Fimage.png?alt=media&amp;token=69ba2f3c-b732-4e9f-b7b5-09f6a73cf84e" alt=""><figcaption></figcaption></figure>

#### **Overview of the Workflow**

1. **Logical Operator Selection (Marker 1)**:
   * Choose between **Any (OR)** to trigger alerts if any condition matches or **All (AND)** to trigger alerts only if all conditions match.
2. **Condition Type (Marker 2)**:
   * Select the type of condition you want to configure. Options include:
     * **Document Classification**: Filter based on categories like Financial or Medical.
     * Other types like Attribute Sensitivity or Labels can also be chosen (not shown here).
3. **Logical Operator for Condition (Marker 3)**:
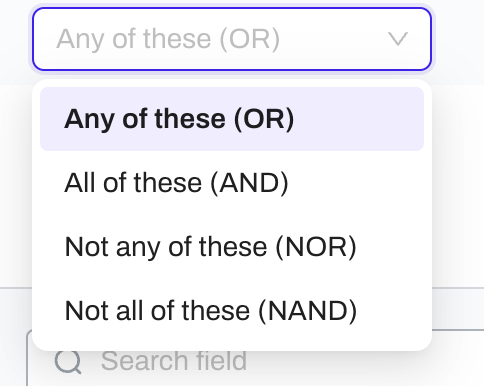
   * Define how the selected condition is evaluated. For **Document Classification**, options include:
     * **Any of these (OR)**: Alerts trigger if a document matches any selected category.
     * **All of these (AND)**: Alerts trigger only if a document matches all selected categories.
4. **Category Selection (Marker 4)**:
   * Expand categories (e.g., Financial, Legal) to view specific subcategories.
5. **Subcategory Options (Marker 5)**:
   * Select subcategories like Tax Forms or Insurance to refine your rule.
6. **Add More Conditions (Marker 6)**:
   * Use the **Add More Condition** button to include additional filters, combining them with the primary logical operator (OR/AND).
7. **Choose a Condition Type**: Select a type like Document Classification, Attribute Type, Attribute Sensitivity, or Labels.
8. **Configure the Selected Condition**: Specify subcategories, instance counts, sensitivity thresholds, or labels.
9. **Add More Conditions (Optional)**: Combine additional conditions to refine your rule set.
10. **Save and Proceed**: Finalize the rule set and move to the next step in the workflow.

***

#### **Step 1: Select the Logical Operator**

<figure><img src="https://682442409-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F0FnJiPbEPpkm5U4tiZUM%2Fuploads%2Fjht9O4QmqCE1pWCAPtBh%2Fimage.png?alt=media&amp;token=97a72372-294c-44a9-92f2-1cec47894609" alt="" width="563"><figcaption></figcaption></figure>

At the top of the screen:

* **Any (OR)**: Triggers alerts if at least one condition is met.
* **All (AND)**: Triggers alerts only if all conditions are met.

This operator applies to all conditions in the rule set.

**Example**:

* Use **OR** for broader policies, such as detecting **Financial OR Legal** documents.
* Use **AND** for stricter policies, such as detecting **Financial AND Medical** documents.

***

#### **Step 2: Add a Condition**

<figure><img src="https://682442409-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F0FnJiPbEPpkm5U4tiZUM%2Fuploads%2Fw7XP5ax5tIH25nDrXN1U%2Fimage.png?alt=media&amp;token=2360789a-cd71-456c-975d-3fb81c1d0fb5" alt="" width="346"><figcaption></figcaption></figure>

1. **Choose a Condition Type** (refer to **Marker 2** in the diagram):
   * **Document Classification**: Apply rules to document categories like Financial or Medical.
   * **Attribute Type**: Filter by sensitive data, such as Credit Card or SSN.
   * **Attribute Sensitivity**: Set thresholds based on sensitivity levels (High, Medium, Low).
   * **Labels**: Apply rules to documents with specific labels like Confidential or Restricted.
2. **Set Logical Operators for Conditions** (refer to **Marker 3** in the diagram):
   * **Any of these (OR)**: Alerts trigger if any selected criteria match.
   * **All of these (AND)**: Alerts trigger only if all criteria match.
   * **Not any of these (NOR)**: Alerts trigger only if none of the selected criteria match.
   * **Not all of these (NAND)**: Alerts trigger if not all criteria match.

***

#### **Step 3: Configure the Selected Condition Type**

<figure><img src="https://682442409-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F0FnJiPbEPpkm5U4tiZUM%2Fuploads%2FtvvKBTTYHS6bUFVAgWCJ%2Fimage.png?alt=media&amp;token=d57c819e-dd3e-46d2-813f-53dbadc583b5" alt="" width="563"><figcaption></figcaption></figure>

**3.1 Document Classification**

Create rules based on document types or categories. Select specific document types to include in or exclude from the rule:

* Broad document categories (e.g., **`Financial, Legal, Human Resource, Medical, Identity, Unclassified`**). &#x20;
* Specific document types within the selected category (e.g., **Invoices/Receipts, Tax Forms, SEC filings**).

**Adding Logical Conditions**

* Use the second dropdown to select the logical operator for this condition. For document classifications, you can choose:
  * **Any of these (OR)**: Alerts trigger if any selected category matches.
  * **All of these (AND)**: Alerts trigger only if all selected categories match.

{% hint style="success" %}
**Tip**: Use buttons like **"Select All"** or **"Clear All"** to manage your selections quickly.
{% endhint %}

{% hint style="info" %}
**Important:** For document classification, only two logical operators are available:

1. "`Any of these (OR`)": Triggers if any of the selected document types are detected.
2. "`Not any of these (NOR`)": Triggers only if all of the selected document types are present.
3. The "`All of these (AND)`" and "`Not all of these (NAND)`" operators are not available for document classification.
4. Document classification can only be applied once in a rule set.
   {% endhint %}

***

**3.2 Attribute Type**

<figure><img src="https://682442409-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F0FnJiPbEPpkm5U4tiZUM%2Fuploads%2F0nmuLyRY2Mu0mmp1PH8W%2Fimage.png?alt=media&amp;token=96fa86a4-6836-47eb-bd06-0cac06b43bc3" alt=""><figcaption></figcaption></figure>

* **Select Attributes**:
  * Choose from predefined sets like **US Essentials** or **Privacy Essentials**.
  * Examples include **SSN**, **Credit Card**, or **Driver’s License**.
* **Set Instance Counts**:
  * Specify **Minimum (Min)** and **Maximum (Max)** counts for each attribute.
  * **Example**: Trigger alerts for documents containing **3–10 Credit Card numbers**.

***

**3.3 Attribute Sensitivity**

<figure><img src="https://682442409-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F0FnJiPbEPpkm5U4tiZUM%2Fuploads%2F98sH7QFgDiQ9QpMjdPPC%2Fimage.png?alt=media&amp;token=fb05c1c8-b450-4268-b0a4-45e12e529f88" alt=""><figcaption></figcaption></figure>

* **Group by Sensitivity**:
  * Configure rules based on **High**, **Medium**, or **Low** sensitivity levels.
* **Set Thresholds**:
  * Example: Trigger an alert for documents with more than 1 **High-Sensitivity attribute and 3 Medium-Sensitivity attributes**.

***

**3.4 Labels**

<figure><img src="https://682442409-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F0FnJiPbEPpkm5U4tiZUM%2Fuploads%2Fwrl4Zk3mJNaqV2OQtjuN%2Fimage.png?alt=media&amp;token=ce915654-5ecf-41b4-be7e-dcb5e2693631" alt=""><figcaption></figcaption></figure>

* **Select Labels**:

  * Expand the label group (e.g., **Lightbeam Sensitivity Labels**) to view available labels.
  * Use checkboxes to select one or more labels (e.g., **Classified**, **Sensitive**, **Restricted**).
  * Use the **Select All** or **Clear All** options for bulk actions.

* **Combine with Other Conditions**:
  * Example: Trigger alerts for **Confidential** documents containing **High-Sensitivity attributes**.

***

#### **Step 4: Add More Conditions**

<figure><img src="https://682442409-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F0FnJiPbEPpkm5U4tiZUM%2Fuploads%2FzLDeiCCu5Ns7GUYYUurX%2Fimage.png?alt=media&amp;token=23c98836-c2b8-4094-a19a-f4f2cadce396" alt="" width="242"><figcaption></figcaption></figure>

* Click **Add More Criteria** to include additional conditions.
* Combine these conditions with the logical operator (OR/AND) selected in Step 1.

**Example**:

* Combine **Document Classification** with **Attribute Sensitivity**:
  * Condition 1: Document Classification > Financial > Tax Forms.
  * Condition 2: Attribute Sensitivity > High > 3 Instances.

***

#### **Step 5: Save and Proceed**

1. Click **Save Criteria** to finalize the rule set.
2. Continue to the next steps:
   * **Step 2: Select Data Sources**: Specify where the rule applies (e.g., Gmail, SharePoint, or S3 buckets).
   * **Step 3: Configure Alerts and Notifications**: Define alert severity and notification preferences.
   * **Step 4: Automation**: Set automated actions for triggered alerts (optional).

***

#### **Example Configurations**

**Example 1: Financial Documents with High-Sensitivity Data**

* Rule: Alert for Financial documents with 5 or more instances of Credit Card numbers.
* Configuration:
  * Condition 1: Document Classification > Financial.
  * Condition 2: Attribute Type > Credit Card > Min 5.

**Example 2: Confidential Documents with Attribute Sensitivity**

* Rule: Alert for Confidential documents containing High-Sensitivity data.
* Configuration:
  * Condition 1: Labels > Confidential.
  * Condition 2: Attribute Sensitivity > High > Min 2.

Click **Next** to move to the next step.<br>

***

### **4. Select Data Sources:**

Users can connect various data sources to the LightBeam application and these data sources would be continuously monitored for attributes and entities.

In the **new update**, the data source selection process has been enhanced with new policy scan conditions. Here's how it works: \
\
a. **Choose the scope of your policy:**

* **All data sources:** This option will automatically include any future data sources in the scanning process. Ideal for policies that should apply universally across your organization's data.<br>

  <figure><img src="https://682442409-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F0FnJiPbEPpkm5U4tiZUM%2Fuploads%2FoawNYsZEJjIO1AMDKZwB%2Fimage.png?alt=media&amp;token=be8d1c4c-6338-4e32-85aa-1cc48b9f2127" alt=""><figcaption></figcaption></figure>
* **Specific Data Source Selection:**&#x20;

  If you don’t want to scan all data sources, deselect the **"Select all data sources"** option and choose specific ones. For each selected data source, you can now configure **more granular scanning conditions**.<br>

  <figure><img src="https://682442409-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F0FnJiPbEPpkm5U4tiZUM%2Fuploads%2FJkA75a1gFyTfs8oOtGJi%2Fimage.png?alt=media&amp;token=fd2f29a1-0e8f-43d5-afef-25cc4c930193" alt=""><figcaption></figcaption></figure>

**b. Configure Granular Controls for Selected Data Sources**<br>

&#x20;   i. **SharePoint:**&#x20;

* **Scan all Sites**: Include all SharePoint sites but specify an **exclusion list** to omit specific sites from scanning.
* **Scan selected Sites**: Target specific sites for scanning by specifying an **inclusion list**.<br>

&#x20;  ii. **Google Drive and OneDrive:**

* Include or exclude **specific drives** (e.g., personal drives, shared drives).

&#x20;   ii&#x69;**. Gmail and Outlook:**&#x20;

* Include or exclude **specific members** or **groups** to target relevant email accounts for scanning.

&#x20;    iv. **Amazon S3:**&#x20;

* Include or exclude **specific buckets** to focus on relevant data repositories.

{% hint style="info" %}
**Limitation**: Folder-level scanning is not supported at this time.
{% endhint %}

**New Features in Alerts 2.1.2**:

* The ability to configure **exclusion lists** for broader data sources such as SharePoint sites, Gmail accounts, and Google Drives.
* The option to automatically include future data sources using the **All Data Sources** setting.

***

**c. Create Inclusion and Exclusion Lists**

For each supported construct (sites, drives, mailboxes, buckets), you can define **detailed inclusion or exclusion lists** to fine-tune the scanning process.

**Example Configuration for SharePoint**:

* If scanning **selected sites**, navigate to the **"Inclusion List for Scanning"** section.
  1. Input the names of the sites to include in the provided text box.
  2. Click the **Add** button to include them in the scanning scope.
  3. If needed, remove sites by selecting their checkboxes and clicking **"Remove from Inclusion List"**.<br>
* If scanning **all sites**, navigate to the **"Exclusion List for Scanning"** section.
  1. Input the names of the sites to exclude in the provided text box.
  2. Click the **Add** button, and ensure their checkboxes are ticked.
  3. Save your configuration by clicking **Save**.

***

**d. Example Scenarios**

**Scenario 1: Apply a Policy to HR Documents in Google Drive**

* **Configuration**:
  1. Select **Google Drive** as the data source.
  2. Include the HR team’s shared drive.
  3. Exclude folders marked **External Collaboration**.
  4. Save the configuration.

**Scenario 2: Monitor Specific Members/Groups in Gmail**

* **Configuration**:
  1. Select **Gmail** as the data source.
  2. Include groups for **HR** and **Legal** teams.
  3. Exclude other groups from the scanning scope.
  4. Save the configuration.

For example, consider this Sharepoint datasource:

<figure><img src="https://682442409-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F0FnJiPbEPpkm5U4tiZUM%2Fuploads%2FtDo4nKGGfPSpds1iYiyW%2Fimage.png?alt=media&amp;token=4e865f47-98c3-4c30-bcc1-06c77999da7d" alt=""><figcaption></figcaption></figure>

<figure><img src="https://682442409-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F0FnJiPbEPpkm5U4tiZUM%2Fuploads%2FuTGDMCMqa2WQr59toT5a%2Fimage.png?alt=media&amp;token=6f2b9163-777c-42b2-a49d-5d6c128d7e40" alt=""><figcaption><p>Figure 12: Select Sites for Scanning</p></figcaption></figure>

Choose between the "**Scan all Sites**" or "**Scan selected Sites**" option:

#### Scan Selected Sites:

* If you selected "**Scan selected Sites**", navigate to the "**INCLUSION LIST FOR SCANNING**" section.<br>
* Input the names of the sites you want to include in scanning in the provided text box.&#x20;

<figure><img src="https://682442409-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F0FnJiPbEPpkm5U4tiZUM%2Fuploads%2F0VWhHnComo54ha2lJqOY%2Fimage.png?alt=media&amp;token=250703fa-29b1-4a71-a308-5e9967bfd148" alt="" width="563"><figcaption><p>Figure 13: Input Sites for Inclusion List</p></figcaption></figure>

* Click on the **Add** button.

<figure><img src="https://682442409-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F0FnJiPbEPpkm5U4tiZUM%2Fuploads%2F1uojt6QSzdjuVHNMFEhP%2Fimage.png?alt=media&amp;token=241b1718-1a10-40a5-b283-ed23b45eb05c" alt="" width="563"><figcaption><p>Figure 14: Add Sites for Inclusion List</p></figcaption></figure>

If needed, you can remove sites from the inclusion list by selecting the checkboxes next to them and clicking the "**Remove from inclusion list**" button.

<figure><img src="https://682442409-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F0FnJiPbEPpkm5U4tiZUM%2Fuploads%2FUbUYxCZoMlMvkVQYae8F%2Fimage.png?alt=media&amp;token=f98d9ef4-e437-4c70-a596-fecf9dd0707c" alt="" width="375"><figcaption><p>Figure 15: Remove Sites from Inclusion List</p></figcaption></figure>

#### Scan All Sites:

* If you select "**Scan all Sites**", you can specify an exclusion list to exclude specific sites from scanning.

<figure><img src="https://682442409-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F0FnJiPbEPpkm5U4tiZUM%2Fuploads%2FEsAQlZuWMJS8R4LV0w79%2Fimage.png?alt=media&amp;token=58ffc0c5-af70-4c09-b85d-7ea2c8f36d0a" alt="" width="563"><figcaption><p>Figure 16: Scan all Sites</p></figcaption></figure>

* If you selected "**Scan all Sites**", navigate to the "**EXCLUSION LIST FOR SCANNING**" section.<br>
* Input the names of the sites you want to exclude from scanning in the provided text box and click on **Add**.

To proceed with the selected sites, make sure their checkboxes are ticked and then click on **Save**.

<figure><img src="https://682442409-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F0FnJiPbEPpkm5U4tiZUM%2Fuploads%2FPmqg4Rq56FKHvJNrEtaP%2Fimage.png?alt=media&amp;token=940c2e5a-f12a-446c-8cc8-7098a2deab38" alt="" width="563"><figcaption><p>Figure 17: Click Save To Scan selected Sites</p></figcaption></figure>

***

### SMB Path Conditions

LightBeam Playbooks Alerts 2.1.2 introduces path conditions for SMB data sources, allowing you to specify which folders should be included in policy scanning. This feature helps you target specific locations within your SMB shares when applying policies.

**Configuring SMB Path Conditions**

To configure SMB path conditions:

1. In the data source selection screen of the rule set creation workflow, select your SMB data source.
2. Click "Select folders" next to the SMB data source to configure path conditions.

Figure 17.1: SMB Data Source Selection

3. In the SMB path configuration dialog, you can choose between:
   * **Scan all folders**: Apply the policy to all folders in the SMB share
   * **Scan selected folders**: Specify an inclusion list of folders to include in scanning

Figure 17.2: SMB Path Conditions Dialog

**Adding Folders to the Inclusion List**

If you selected "Scan selected folders", follow these steps to add folders to the inclusion list:

1. Navigate to the "INCLUSION LIST FOR SCANNING" section.
2. Enter the folder path in the text field (e.g., "/Shared3/Finance/").
3. Click the "Add" button.

Figure 17.3: Adding Folders to Inclusion List

4. The folder will appear in the inclusion list with a checkbox.
5. Ensure the checkbox is selected for folders you want to include.
6. If needed, you can remove folders from the inclusion list by selecting the checkboxes next to them and clicking the "Remove from inclusion list" button.
7. Click "Save" to confirm your selection.

**Excluding Folders from Scanning**

If you selected "Scan all folders", you can specify an exclusion list:

1. Navigate to the "EXCLUSION LIST FOR SCANNING" section.
2. Enter the folder path you want to exclude from scanning in the provided text box.
3. Click the "Add" button.
4. Ensure the checkboxes are ticked for folders you want to exclude.
5. Click "Save" to confirm your selection.

> **Note**: Only documents in the specified folders (or all folders except excluded ones) will be evaluated against the policy criteria, helping to optimize scanning performance and reduce false positives.

**Benefits of SMB Path Conditions**

* **Targeted Scanning**: Focus policy evaluation on specific folders containing sensitive data
* **Improved Performance**: Reduce scanning time by excluding irrelevant folders
* **Granular Control**: Apply different policies to different folders within the same SMB share
* **Reduced False Positives**: Limit policy application to relevant data locations

***

### 5. Set Alert & Regulations

LightBeam Spectra scans the selected data source(s) for specified attribute sets and raises an alert for each instance of data violation. In this step, you'll configure how these alerts are generated, managed, and prioritized. Here's how to set up each option:<br>

<figure><img src="https://682442409-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F0FnJiPbEPpkm5U4tiZUM%2Fuploads%2FlQ27QXDKTlvIRbVWimjM%2Fimage.png?alt=media&amp;token=8c66e955-d532-4ef7-be48-6677bd6f261a" alt=""><figcaption></figcaption></figure>

#### Enable Alerts

* Select the **Enabled** option to receive alerts for this rule set.
* Choose **Disabled** if you don't want to generate alerts.
* When enabled, an alert is triggered for each data privacy violation detected.

#### Assign Alerts

* By default, alerts are assigned to the Datasource Owner(s).
* To assign alerts to the Object Owner(s) instead, select that option.

#### Add Additional Recipients

* To include more team members in alert notifications:
  1. Locate the field labeled "`Hit enter to add another member`".
  2. Type in the email address of each additional recipient.
  3. Press Enter after each email to add it to the list.

#### Set Alert Severity

* Choose the severity level for alerts generated by this rule set.
* Click the **Select Severity Level** dropdown menu and choose one of:
  * **Info**: For low-priority notifications
  * **Warning**: For moderate-priority issues
  * **Critical**: For high-priority alerts requiring immediate attention
* Selecting the appropriate severity helps prioritize responses to alerts.

<figure><img src="https://682442409-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F0FnJiPbEPpkm5U4tiZUM%2Fuploads%2FunHs0SDHUQjYA3tQ5xRH%2Fimage.png?alt=media&amp;token=a9f3bf33-e0c1-4f78-bad2-c99f60f9fc25" alt="" width="375"><figcaption></figcaption></figure>

#### Link to Regulations (Optional)

* If the rule set relates to specific data privacy regulations:
  1. Click the **Select Regulations** dropdown.
  2. Choose the relevant regulations from the list.
* This optional field allows you to associate alerts with specific data privacy regulations that may be breached.
* Linking regulations aids in compliance tracking and reporting.

By carefully configuring these settings, you ensure that the right people are promptly notified of potential data privacy violations, can prioritize their responses effectively, and maintain regulatory compliance as needed.

***

### **6. Automation (Optional)**

The option to automate actions on alerts that highlight instances of data breaches will be made available in the future.

This feature will allow the system to automatically act on the alert and prevent the violation through actions such as:

* **Redaction**
* **Deletion**
* **Revoking access**
* **Archiving**

<img src="https://682442409-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F0FnJiPbEPpkm5U4tiZUM%2Fuploads%2FGWlyebHhltJCyzLTx4vU%2F19.png?alt=media" alt="Figure 22: Automation" width="375">

***

### [File Classification-based Policies](#file-classification-based-policies)

LightBeam Playbooks Alerts 2.1.1 introduces file classification-based policies, which allow you to apply labels and generate alerts based on the specific file classification of documents. These policies leverage the categorization of files determined by LightBeam Spectra's machine-learning algorithms, enabling more granular control over labeling and alerting based on the file classification hierarchy.

#### Creating a Labeling Policy with File Classification-based Labels

1. Navigate to the **Policies** section within the LightBeam Spectra console.<br>

2. Click on the "**Create New**" button to start creating a new **Labeling Policy**.<br>

   <figure><img src="https://682442409-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F0FnJiPbEPpkm5U4tiZUM%2Fuploads%2FZM11seHkDzm9SSW0pM9S%2Fimage.png?alt=media&amp;token=cd0e8a73-991b-40c5-956f-fafa74a796e0" alt=""><figcaption></figcaption></figure>

   <br>

3. Provide a name for the policy in the "`Rule Set Name`" field.<br>

   <figure><img src="https://682442409-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F0FnJiPbEPpkm5U4tiZUM%2Fuploads%2F1MvHLoC6J008AAGGqaoA%2Fimage.png?alt=media&amp;token=e41d2caf-77cf-4a6e-a35f-b48f5bcda25a" alt=""><figcaption></figcaption></figure>

4. Select the file classification-based label set that you want to use from the available options.\
   &#x20;\
   (Refer to the [Label Management](/lxqobxw6ak7CTnsQjikH/core-features/spectra-ai/insights/label-management.md) document for instructions on creating file classification-based label sets.)\
   \
   Click on **Next.**<br>

   <figure><img src="https://682442409-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F0FnJiPbEPpkm5U4tiZUM%2Fuploads%2FnHDSd7acXnWVMxP2iyPp%2Fimage.png?alt=media&amp;token=f1e8e643-6683-45ea-ade4-aa0beba04193" alt=""><figcaption></figcaption></figure>

5. Choose the data sources to which the policy should be applied, such as SharePoint, OneDrive, or Google Drive.<br>

   <figure><img src="https://682442409-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F0FnJiPbEPpkm5U4tiZUM%2Fuploads%2F9OHL2SjTBFj0zcacOwfR%2Fimage.png?alt=media&amp;token=c104bca8-d653-4ffb-8178-d7ca87238f0e" alt=""><figcaption></figcaption></figure>

6. Click on the "**Save & Close**" button to save the Labeling Policy.<br>

   <figure><img src="https://682442409-files.gitbook.io/~/files/v0/b/gitbook-x-prod.appspot.com/o/spaces%2F0FnJiPbEPpkm5U4tiZUM%2Fuploads%2FBMzOtas5XgP8ibLWQ1Mb%2Fimage.png?alt=media&amp;token=8ad64abb-bb52-4285-ac11-50f5d47a9945" alt="" width="375"><figcaption></figcaption></figure>


---

# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.

## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation dynamically by asking a question.

Perform an HTTP GET request on the current page URL with the `ask` query parameter, and the optional `goal` query parameter:

```
GET https://docs.lightbeam.ai/lxqobxw6ak7CTnsQjikH/core-features/spectra-ai/playbooks/policy-and-alerts/how-to-create-a-rule-set.md?ask=<question>&goal=<endgoal>
```

`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is optional and describes the broader end goal you are ultimately trying to accomplish on behalf of the user. GitBook uses it to tailor the answer towards what is most useful for that goal.

The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.

Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.